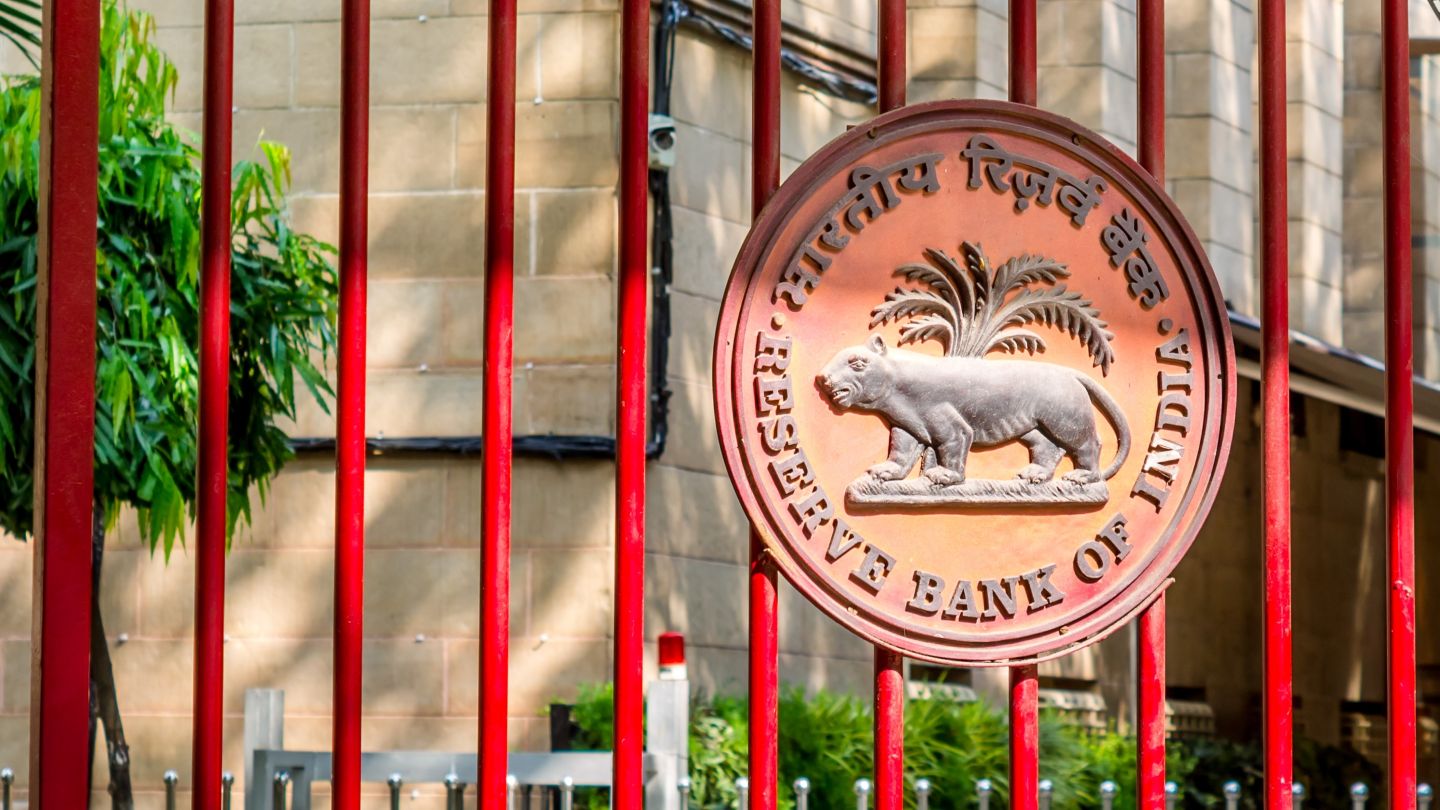
The Reserve Bank of India (RBI) has asked banks to provide evidence that they are meeting cybersecurity requirements and to explain their preparedness for risks linked to AI, Reuters reported citing sources.
The regulator’s action follows a series of cyber incidents affecting India’s financial sector.
Go deeper with GlobalData
Access deeper industry intelligence
Experience unmatched clarity with a single platform that combines unique data, AI, and human expertise.
In recent meetings, the RBI told banks to assess security gaps in application programming interfaces (APIs).
These software connections enable banks to link with non-bank lenders and fintechs, three sources said.
One person familiar with regulatory thinking said attackers consider smaller lenders, non-bank lenders, and third-party vendors to be “softer targets”.
The RBI has already issued directions on cybersecurity risk management.
However, their implementation remains incomplete in some cases, according to a consultant working with top banks.
The regulator is therefore seeking stronger execution of those requirements.
Recent incidents have included a data leak involving 3,900 customers of State Bank of India, the country’s largest lender.
The bank said last week that it was investigating the matter and had not identified the vulnerability involved.
In a separate case, two Mumbai-based non-bank lenders lost about $2m through more than 700 unauthorised instant transfers from accounts held with ICICI Bank on 8-9 October, according to a police complaint reviewed by Reuters.
The complaint stated that hackers had compromised the API link used to send loan disbursal instructions to ICICI Bank.
CERT-In, India’s cyber agency, warned that hackers were obtaining banks’ API credentials to transfer money from lenders’ own systems. It said AI-assisted tools may be involved.
The agency also said on X earlier this week that it had conducted cybersecurity training for 300 officials from more than 55 financial institutions.