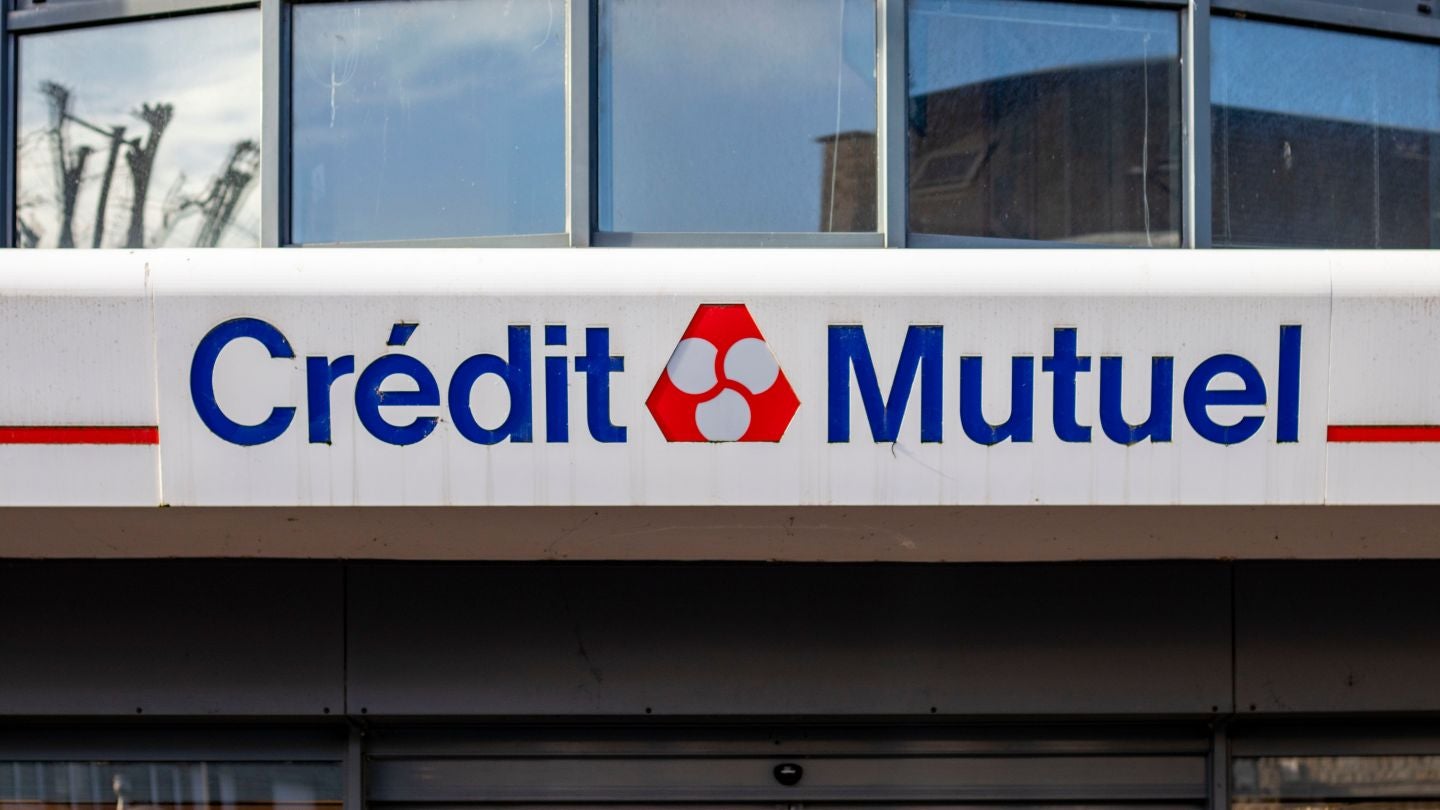
Crédit Mutuel Arkéa has reported being the “victim” of an attack that resulted in fraudulent fund transfers, according to the translated version of disclosures issued by the French bank.
The breach occurred when external perpetrators penetrated the platform of an external service provider to gain direct access to the banking group.
Go deeper with GlobalData
Access deeper industry intelligence
Experience unmatched clarity with a single platform that combines unique data, AI, and human expertise.
Arkéa rejected claims that any “entry” was secured through its digital subsidiary Fortuneo, while also ruling out employee error.
The perpetrators conducted transactions using Arkéa’s own corporate account rather than individual customer accounts.
Capital was shifted to outside banking entities, with the attackers potentially converting these proceeds into cryptocurrency through specialised trading platforms.
The group stated that the incident carried “no impact” on customer assets, confirming that clients across its federations and subsidiaries incurred no financial losses.
The primary customer-facing disruption was limited to execution delays affecting select transfer orders.
Asked whether €118m ($133m) had been siphoned off during the breach, Arkéa declined to validate the specific amount, confirming solely the general order of magnitude.
The bank noted that while it is “still too early” to publish a definitive total, the losses under review will not jeopardise its broader financial health or stability.
Upon spotting the unauthorised activity, the group reported the breach to regulatory and supervisory authorities and temporarily halted specific transaction channels to block secondary fraudulent flows.
Arkéa noted the incident is now closed and “under control”, with operational activities resuming incrementally alongside the deployment of heightened security protocols.
Judicial and police authorities are now reviewing the case alongside Arkéa’s technical units to pinpoint the origin of the intrusion and establish the exact modus operandi.
The bank advised its client base to monitor accounts for potential phishing communications.
Customers were cautioned against disclosing confidential records including login usernames, passwords, payment card numbers, and SMS validation codes and directed to confirm suspicious correspondence with branch advisors.